https://www.whiteready.com/it/ottenuta-la-certificazione-di-parita-di-genere/
Tested 2026-10-17 05:10:17 using Chrome 154.0.8037.57 (runtime settings)
This page is fast to paint and snappy to interact with, but prone to layout shifts, loose on best practices and weak on user privacy.
Visual metrics
Google Web Vitals
The page ships 22 images (out of 22) in JPEG/PNG/GIF without a modern alternative. Wrap them in a <picture> with a <source type="image/avif"> or "image/webp" before the legacy <img>, or serve modern formats from your image pipeline directly. AVIF and WebP usually deliver 25–50% smaller files at the same quality.
The total JavaScript transfer size is 354.2 kB and the uncompressed size is 1.2 MB. This is totally crazy! There is really room for improvement here.
The page has 7 requests that are missing a cache time. Configure a cache time so the browser doesn't need to download them every time. It will save 26.4 kB the next access.
Timings summary
| Metric | Min | Median | Mean | Max | Runs agree? |
|---|---|---|---|---|---|
| First visual change | 968 ms | 1.066 s | 1.045 s | 1.100 s | varies ±6% |
| Last visual change | 1.902 s | 2.000 s | 2.045 s | 2.233 s | varies ±8% |
| Speed index | 1.024 s | 1.111 s | 1.099 s | 1.163 s | varies ±6% |
| Visual readiness | 934 ms | 934 ms | 1.000 s | 1.133 s | runs disagree ±11% |
| Visual complete 85 | 1.035 s | 1.100 s | 1.100 s | 1.166 s | varies ±6% |
| Visual complete 95 | 1.202 s | 1.300 s | 1.278 s | 1.333 s | varies ±5% |
| Visual complete 99 | 1.902 s | 2.000 s | 2.045 s | 2.233 s | varies ±8% |
Run 3 SpeedIndex median
The red band on the timeline marks when the main thread was busy with long tasks: moments when the page could not paint or respond, however the video looks.
Download videoUse --filmstrip.showAll to show all filmstrips.
Click a frame to seek the video to that moment. The dot marks frames where the page changed visually.
Rendering was not meaningfully delayed. First paint landed at 1.048 s on a 795 ms first byte; the 7 render-blocking requests were done by 889 ms and the remaining ~159 ms is style, layout and web-font loading.
Want to see how much CSS style-recalculation work delayed FCP and LCP, plus CPU long tasks? Run with --cpu.
Blocking requests delay both paints: the browser renders nothing until they arrive, so they push First Contentful Paint and everything after it, including the largest paint (LCP). Requests that block the parser inside the body stall everything after them in the document. Load JavaScript with defer or async, and keep non-critical CSS off the critical path with media attributes. Bars show when each request loaded on a clock that runs to the last paint; the gap after the bars is style and layout work. Web fonts are context, not blockers: text renders invisible or in a fallback face while they load, so a font finishing after a paint is the classic reason text changed late.
| Request | When it loaded | Transfer | Download |
|---|---|---|---|
document | 794 ms | 25.8 KB | 793 ms |
post-2631.cssblocking | 68 ms | 1.2 KB | 68 ms |
style.cssblocking | 42 ms | 2.0 KB | 42 ms |
mfn-local-fonts.cssblocking | 39 ms | 753 B | 39 ms |
responsive.min.cssblocking | 38 ms | 10.0 KB | 38 ms |
be.min.cssblocking | 37 ms | 72.6 KB | 37 ms |
fontawesome.min.cssblocking | 36 ms | 12.8 KB | 36 ms |
script.jsblocking | 36 ms | 9.0 KB | 36 ms |
jquery.min.jsblocks parser in body | 64 ms | 30.0 KB | 64 ms |
| 13 more requests | all done by 956 ms | 58.2 KB | |
26 ms | 18.7 KB | 26 ms | |
26 ms | 8.2 KB | 26 ms | |
loaded after FCP, at 1.136 s | 71.3 KB | 19 ms | |
0262 ms524 msFCP · LCP 1.048 s |
The coach helps you find performance problems on your web page using web performance best practice rules. And gives you advice on privacy and best practices. Tested using Coach-core version 9.2.1.
modernImageFormatsThe page ships 22 images (out of 22) in JPEG/PNG/GIF without a modern alternative. Wrap them in a <picture> with a <source type="image/avif"> or "image/webp" before the legacy <img>, or serve modern formats from your image pipeline directly. AVIF and WebP usually deliver 25–50% smaller files at the same quality.
AVIF and WebP routinely deliver 25–50% smaller files than JPEG and PNG at the same perceived quality, and every browser version still under support understands at least one of them. Ship modern formats either through a <picture> element with <source type="image/avif"> / "image/webp" entries in front of the legacy <img>, or directly from a content-negotiating image pipeline that returns AVIF / WebP when the client accepts it. https://web.dev/articles/serve-images-webp
javascriptSizeThe total JavaScript transfer size is 354.2 kB and the uncompressed size is 1.2 MB. This is totally crazy! There is really room for improvement here.
A lot of JavaScript often means you are downloading more than you need. How complex is the page and what can the user do on the page? Do you use multiple JavaScript frameworks?
cacheHeadersThe page has 7 requests that are missing a cache time. Configure a cache time so the browser doesn't need to download them every time. It will save 26.4 kB the next access.
The easiest way to make your page fast is to avoid doing requests to the server. Setting a cache header on your server response will tell the browser that it doesn't need to download the asset again during the configured cache time! Always try to set a cache time if the content doesn't change for every request.
cssSizeThe total CSS transfer size is 101.7 kB and uncompressed size is 592.4 kB. That is big and the CSS could most probably be smaller.
Delivering a massive amount of CSS to the browser is not the best thing you can do, because it means more work for the browser when parsing the CSS against the HTML and that makes the rendering slower. Try to send only the CSS that is used on that page. And make sure to remove CSS rules when they aren't used anymore.
fewFontsThe page has 5 font requests. Do you really need them? What value does the fonts give the user?
How many fonts do you need on a page for the user to get the message? Fonts can slow down the rendering of content, try to avoid loading too many of them because worst case it can make the text invisible until they are loaded (FOIT—flash of invisible text), best case they will flicker the text content when they arrive.
cacheHeadersLongThe page has 45 requests that have a shorter cache time than one year (but still a cache time).
Setting a cache header is good. Setting a long cache header (a year) is even better because the asset will stay in the browser cache across visits. For content-hashed URLs (e.g. app.4af2.css) you can safely use Cache-Control: max-age=31536000, immutable. For unversioned URLs that may change, use a revalidating strategy instead.
decodingAsyncThe page has 12 images (out of 27) without a decoding hint. Add decoding="async" to non-critical images so the browser can decode them off the main thread.
Setting decoding="async" on an <img> tells the browser it can decode the image off the main thread, which keeps the page responsive to user interactions while images are being processed. The default ("auto") leaves the choice to the browser. https://developer.mozilla.org/en-US/docs/Web/HTML/Element/img#decoding
longTasksThe page has 2 CPU long tasks with the total of 174 ms. The total blocking time is 62 ms and 1 long task before first contentful paint with total time of 62 ms. However the CPU Long Task is depending on the computer/phones actual CPU speed, so you should measure this on the same type of the device that your user is using. Use Geckoprofiler for Firefox or Chromes tracelog to debug your long tasks.
Long CPU tasks locks the thread. To the user this is commonly visible as a "locked up" page where the browser is unable to respond to user input; this is a major source of bad user experience on the web today. However the CPU Long Task is depending on the computer/phones actual CPU speed, so you should measure this on the same type of the device that your user is using. To debug you should use the Chrome timeline log and drag/drop it into devtools or use Firefox Geckoprofiler.
avoidScalingImagesThe page has 3 images that are scaled more than 100 pixels. It would be better if those images are sent so the browser don't need to scale them.
It's easy to scale images in the browser and make sure they look good in different devices, however that is bad for performance! Scaling images in the browser takes extra CPU time and will hurt performance on mobile. And the user will download extra kilobytes (sometimes megabytes) of data that could be avoided. Don't do that, make sure you create multiple version of the same image server-side and serve the appropriate one.
lazyLoadingImagesThe page has 3 below-the-fold images without loading="lazy". Add loading="lazy" so the browser defers downloading and decoding them until the user scrolls them into view.
Adding loading="lazy" to an <img> tells the browser not to download or decode it until it is close to the viewport. For images that the user may never see (deep in the page, behind a tab, in a footer carousel), this saves bandwidth and main-thread time during initial render. The LCP image and any image in the initial viewport should NOT be lazy-loaded — that delays the first paint. https://developer.mozilla.org/en-US/docs/Web/HTML/Element/img#loading
avoidRenderBlockingThe page has 7 blocking requests and 0 in body parser blocking (1 JavaScript and 6 CSS).
The critical rendering path is what the browser needs to do to start rendering the page. Every file requested inside of the head element will postpone the rendering of the page, because the browser need to do the request. Avoid loading JavaScript synchronously inside of the head (you should not need JavaScript to render the page), request files from the same domain as the main document (to avoid DNS lookups) and inline CSS for really fast rendering and a short rendering path.
spofThe page has 1 request inside of the head that can cause a SPOF (single point of failure). Load them asynchronously or move them outside of the document head.
A page can be stopped from loading in the browser if a single JavaScript, CSS, and in some cases a font, couldn't be fetched or is loading really slowly (the white screen of death). That is a scenario you really want to avoid. Never load 3rd-party components synchronously inside of the head tag.
optimalCssSizehttps://www.whiteready.com/wp-content/themes/betheme/css/be.min.css?ver=28.3.1 size is 74.3 kB (74297) and that is bigger than the limit of 25 kB. Try to keep each CSS response under 25 kB.
Render-blocking CSS holds up the first paint until it has fully downloaded, parsed and applied, so smaller CSS files mean a faster start. Split your CSS into a small critical bundle inlined or eagerly loaded, with the rest lazy-loaded.
| URL | Transfer | Content |
|---|---|---|
| https://www.whiteready.com/wp-content/themes/betheme/css/be.min.css?ver=28.3.1 | 72.6 KB | 450.4 KB |
inlineCssThe page has both inline CSS and CSS requests even though it uses a HTTP/2-ish connection. If you have many users on slow connections, it can be better to only inline the CSS. Run your own tests and check the waterfall graph to see what happens.
In the early days of the Internet, inlining CSS was one of the ugliest things you can do. That has changed if you want your page to start rendering fast for your user. Always inline the critical CSS when you use HTTP/1 and HTTP/2 (avoid doing CSS requests that block rendering) and lazy load and cache the rest of the CSS. It is a little more complicated when using HTTP/2. Does your server support HTTP push? Then maybe that can help. Do you have a lot of users on a slow connection and are serving large chunks of HTML? Then it could be better to use the inline technique, becasue some servers always prioritize HTML content over CSS so the user needs to download the HTML first, before the CSS is downloaded.
metaDescriptionThe page is missing a meta description.
Use a page description to make the page more relevant to search engines.
unnecessaryHeadersThere are 41 responses that sets both a max-age and expires header. There are 14 responses that sets a server header.
Do not send headers that you don't need. We look for p3p, cache-control and max-age, pragma, server and x-frame-options headers. Have a look at Andrew Betts - Headers for Hackers talk as a guide https://www.youtube.com/watch?v=k92ZbrY815c or read https://www.fastly.com/blog/headers-we-dont-want.
cumulativeLayoutShiftYou have a cumulative layout shift score (0.1648) that needs improvements. It is in the Google Web Vitals needs improvement range, shift higher than 0.1. You should manually check the filmstrip or video and check if it will affect the user.
Cumulative Layout Shift measures the sum total of all individual layout shift scores for unexpected layout shift that occur. The metric is measuring visual stability by quantify how often users experience unexpected layout shifts. It is one of Google Web Vitals.
pageTitleThe title is too long by 33 characters. The recommended max is 60
Use a title to make the page more relevant to search engines.
thirdPartyThe page do 26% requests to third party domains (14 requests and 279.4 kB). First party is 40 requests and 651 kB. The regex .*whiteready.* was used to calculate first/third party requests.
Do not load most of your content from third party URLs.
referrerPolicyNo <meta name="referrer"> tag was found on the page. Set a Referrer-Policy response header (preferred) or add a meta tag, for example <meta name="referrer" content="strict-origin-when-cross-origin">.
Without an explicit referrer policy the browser falls back to the user-agent default and may leak the full URL of the previous page (including query strings) to every cross-origin request. Set a Referrer-Policy response header (preferred) or a <meta name="referrer"> tag in the document. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Referrer-Policy
contentSecurityPolicyHeaderSet a Content-Security-Policy header to mitigate cross-site scripting attacks. You can start with a Content-Security-Policy-Report-Only header, which only reports violations rather than blocking them.
A Content-Security-Policy response header tells the browser which sources of script, style, and other content are allowed. The most effective form is a strict CSP using nonces or hashes together with strict-dynamic; the worst is a missing header, with unsafe-inline and unsafe-eval close behind. https://web.dev/articles/strict-csp
crossOriginEmbedderPolicyHeaderSet a Cross-Origin-Embedder-Policy header (typically require-corp or credentialless) on the document response to control cross-origin embedding.
Cross-Origin-Embedder-Policy (COEP) makes the page refuse to load cross-origin subresources unless they explicitly opt in via CORP or CORS. Together with Cross-Origin-Opener-Policy it puts the page in a cross-origin isolated context, which mitigates cross-window side-channel attacks (Spectre) and unlocks high-resolution timers and SharedArrayBuffer. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Cross-Origin-Embedder-Policy
crossOriginOpenerPolicyHeaderSet a Cross-Origin-Opener-Policy header (typically same-origin) on the document response to isolate the page from cross-origin windows.
Cross-Origin-Opener-Policy (COOP) lets a page sever its window-group ties to cross-origin documents that opened it or that it opens. Together with Cross-Origin-Embedder-Policy it puts the page in a cross-origin isolated context, which mitigates cross-window side-channel attacks (Spectre) and unlocks high-resolution timers and SharedArrayBuffer. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Cross-Origin-Opener-Policy
crossOriginResourcePolicyHeaderSet a Cross-Origin-Resource-Policy header (same-origin, same-site or cross-origin) on the document response to limit who may embed it.
Cross-Origin-Resource-Policy (CORP) is a per-response opt-in that tells the browser which origins are allowed to embed the resource. It blocks cross-origin or cross-site no-cors embedding (img, script, iframe, etc.) and is one of the building blocks of cross-origin isolation. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Cross-Origin-Resource-Policy
nelHeaderSet a NEL header (paired with Reporting-Endpoints) to collect connection-level error reports from the field.
The NEL (Network Error Logging) response header tells the browser to record connection-level failures (DNS, TLS, HTTP errors) and ship them to a reporting endpoint. NEL pairs with the Reporting-Endpoints / Report-To header — the page declares the endpoint group and NEL points at it. Together they give you visibility into errors that never reach your origin server. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/NEL
permissionsPolicyHeaderSet a Permissions-Policy header to control which browser features the page can use.
The Permissions-Policy response header (the successor to Feature-Policy) lets a site explicitly opt in or out of powerful browser features such as camera, microphone, geolocation, payment and clipboard. Setting a strict policy reduces the attack surface and limits what embedded third parties can do. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Permissions-Policy
reportingEndpointsHeaderSet a Reporting-Endpoints header (or the legacy Report-To header) so CSP reports, NEL data and other Reporting-API events have an endpoint to land at.
The Reporting-Endpoints response header (the successor to Report-To) names the URLs that browsers should POST reports to. Without it, CSP report-to directives, Cross-Origin-Opener-Policy reports, NEL data and other Reporting-API events have nowhere to go. The legacy Report-To header is still accepted for older Chromium versions. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Reporting-Endpoints
xContentTypeOptionsHeaderSet X-Content-Type-Options: nosniff on the document response to prevent MIME-sniffing.
X-Content-Type-Options: nosniff prevents browsers from interpreting files as a different MIME type than what is declared in the Content-Type header. This blocks a class of cross-site scripting and content-type confusion attacks and should be set on every response. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/X-Content-Type-Options
strictTransportSecurityHeaderA strict transport header is set but miss out on setting includeSubDomains
The HTTP Strict-Transport-Security response header (often abbreviated as HSTS) lets a web site tell browsers that it should only be accessed using HTTPS, instead of using HTTP. https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Strict-Transport-Security.
thirdPartyPrivacyThe page has 4% requests that are 3rd party (2 requests with a size of 248 kB). The page do 2 utility requests and uses 1 utility tool.
Using third party requests shares user information with that third party. Please avoid that! The project https://github.com/patrickhulce/third-party-web is used to categorize first/third party requests.
A snapshot of what the browser actually built for this page: the document, how big and deep the DOM tree is and what it kept in storage. Big, deep trees are slower to style and lay out, so the counts Chrome warns about carry a flag.
Document
What the page says it is and how large it rendered.
DOM structure
How much markup the browser has to build, style and lay out.
What the page stored on the client, and the network it was tested on.
Data collected using
Coach-core version 9.2.1. With updated code from
Webappanalyzer 2026-05-04. Use
--browsertime.firefox.includeResponseBodies html or
--browsertime.chrome.includeResponseBodies html to help Wappalyzer find more information about technologies used.
Data collected using Third Party Web version 0.29.2.
Data from run 3
0.0s1.1s1.2s1.4s1.5s1.7s1.8s2.0sWhen the page main content is rendered, collected via the Largest Contentful Paint API. Read more about Largest Contentful Paint.
body > div#Wrapper > div#Content > div > main > div > section:eq(1) > div:eq(1) > div > div > div:eq(1) > div > p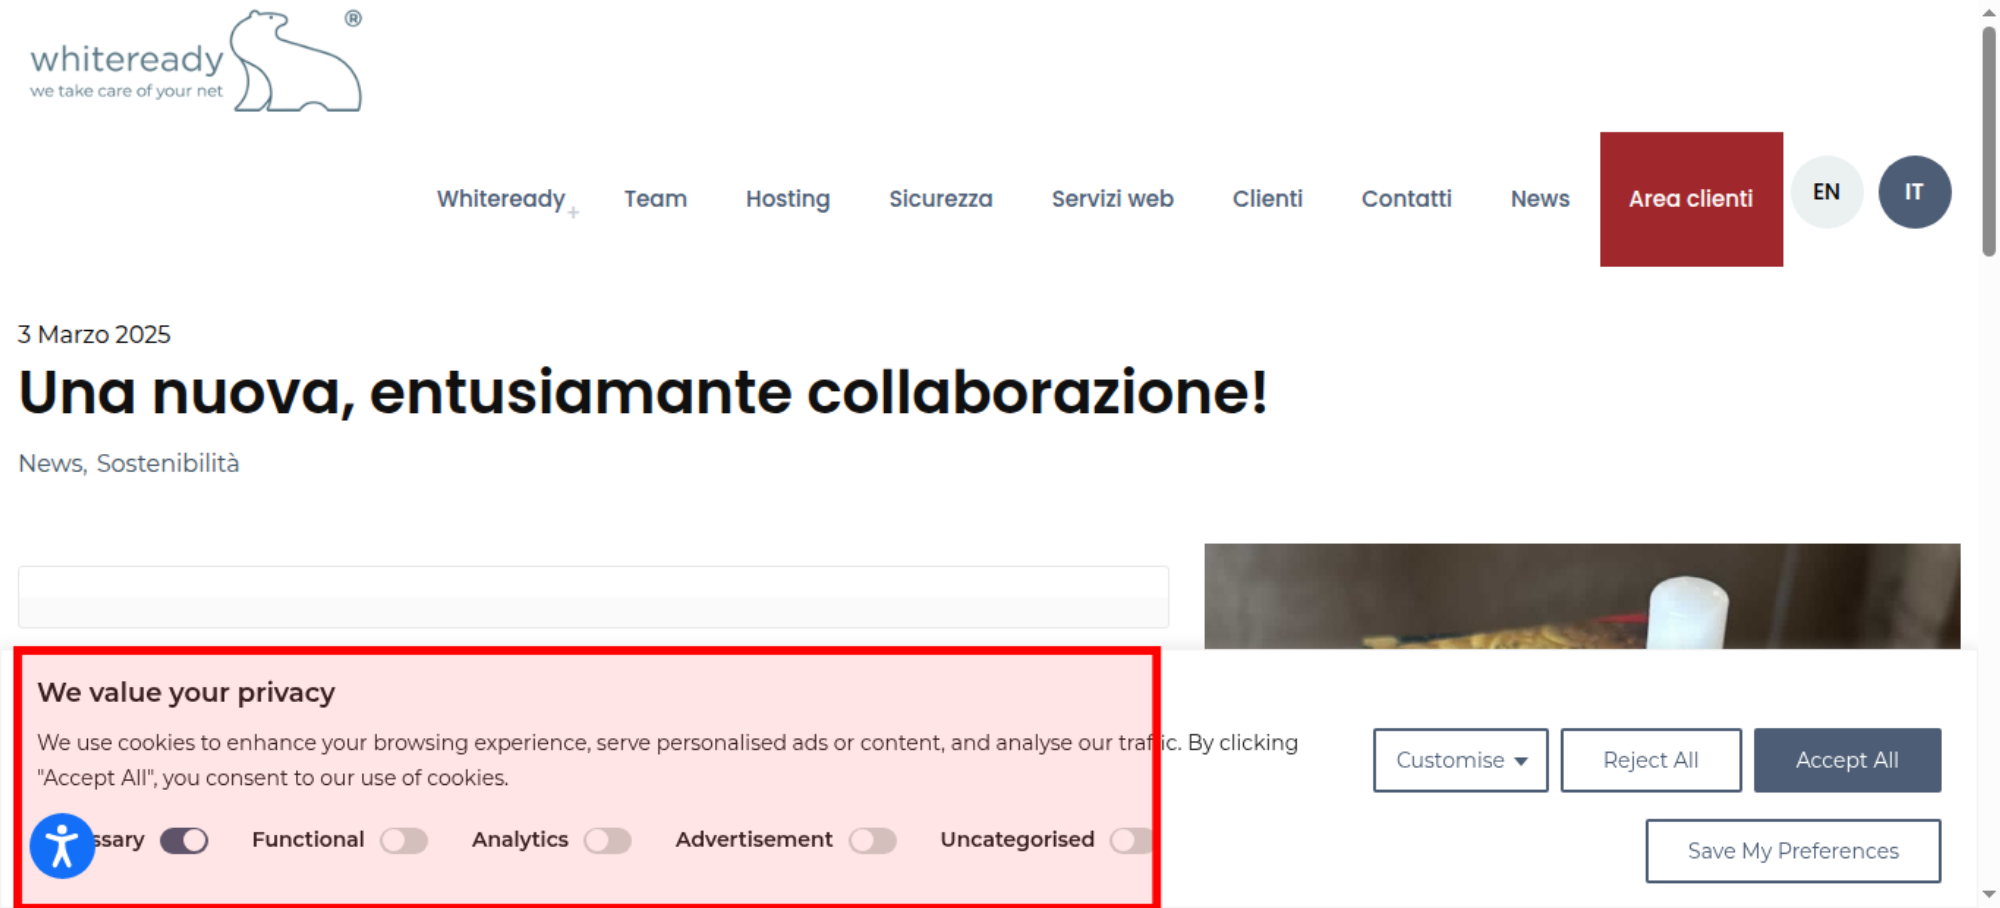
The LCP element is highlighted in the screenshot. If nothing is highlighted the element was removed before the screenshot or the LCP API couldn't find it.
How much the page's content shifts as it loads, collected via the Cumulative Layout Shift API.
One shift is 100% of your 0.165 CLS. div#Content moved at 1.063 s. Reserve space for whatever renders into that spot, a fixed height or an aspect-ratio box, so later content stops pushing the page around.
Worst first, showing shifts of 0.01 and up. Each percentage is that shift's exact share of the score.
body > div#Wrapper > div#Contentbody > div#Wrapper > div#Header_wrapper > header#Header > div#Top_bar > div > div > div:eq(0) > div:eq(1)body > div#Wrapper > div#Content > div > main > div > section:eq(1) > div:eq(1) > div > div > div:eq(1) > div > p > #text:eq(3)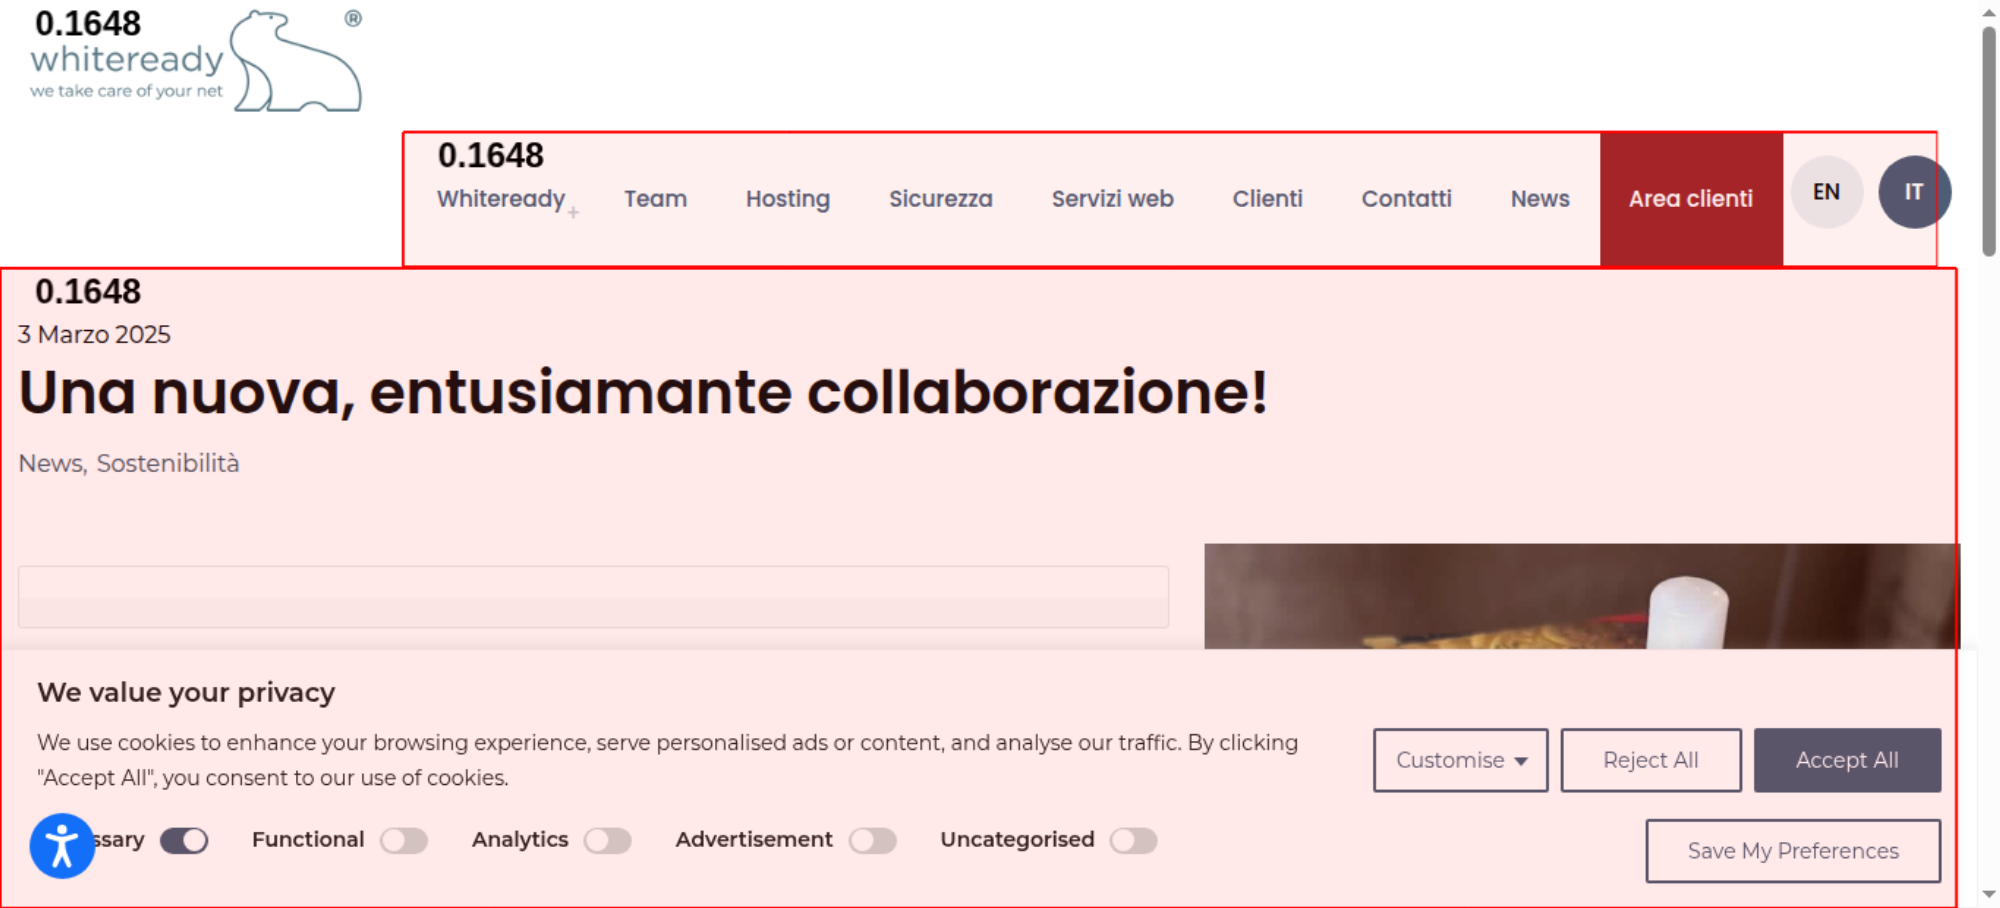
Elements that shifted by more than 0.01 are highlighted in the screenshot. If an element shifted outside the viewport, it won't appear here. Check the video or filmstrip to see the shift.
There are no custom configured scripts.
There are no custom extra metrics from scripting.
How the page is built.
https://www.whiteready.com/it/ottenuta-la-certificazione-di-parita-di-genere/
| Header | Value |
|---|---|
content-encoding | gzip |
content-length | 25837 |
content-type | text/html; charset=UTF-8 |
date | Sat, 17 Oct 2026 05:11:03 GMT |
link | <https://www.whiteready.com/wp-json/>; rel="https://api.w.org/", <https://www.whiteready.com/wp-json/wp/v2/posts/2398>; rel="alternate"; title="JSON"; type="application/json", <https://www.whiteready.com/?p=2398>; rel=shortlink |
referrer-policy | no-referrer-when-downgrade |
strict-transport-security | max-age=63072000; preload |
vary | Accept-Encoding |
x-cache-status | MISS |
x-endurance-cache-level | 2 |
x-nginx-cache | WordPress |
x-served-by | www.whiteready.com |
Transfer size908.7 KB
Content size2.3 MB
Requests54
| Content | Header Size | Transfer Size | Content Size | Requests |
|---|---|---|---|---|
| html | 0 b | 25.8 KB | 138.2 KB | 1 |
| css | 0 b | 99.3 KB | 578.5 KB | 6 |
| javascript | 0 b | 345.9 KB | 1.2 MB | 17 |
| image | 0 b | 298.5 KB | 293.4 KB | 15 |
| font | 0 b | 124.9 KB | 122.9 KB | 5 |
| plain | 0 b | 260 B | 2 B | 1 |
| json | 0 b | 10.3 KB | 44.3 KB | 6 |
| svg | 0 b | 3.7 KB | 7.3 KB | 3 |
| Total | 0 b | 908.7 KB | 2.3 MB | 54 |
| Domain | Total download time | Transfer Size | Content Size | Requests |
|---|---|---|---|---|
| www.whiteready.com | 2.173 s | 635.8 KB | 1.4 MB | 40 |
| cdn-cookieyes.com | 195 ms | 29.1 KB | 97.8 KB | 9 |
| log.cookieyes.com | 71 ms | 260 B | 2 B | 1 |
| embeds.acswapp.com | 57 ms | 1.3 KB | 1.1 KB | 2 |
| eu.acsbapp.com | 55 ms | 241.2 KB | 891.7 KB | 1 |
| eu-cdn.acsbapp.com | 263 ms | 1.0 KB | 987 B | 1 |
| type | min | median | max |
|---|---|---|---|
| Expires | 0 seconds | 4 weeks | 4 weeks |
| Last modified | 16 hours | 4 weeks | 1 year |
Includes requests done after load event end.
| Content | Transfer Size | Requests |
|---|---|---|
| html | 0 b | 0 |
| css | 0 b | 0 |
| javascript | 241.2 KB | 1 |
| image | 9.5 KB | 2 |
| font | 0 b | 0 |
| favicon | 0 b | 0 |
| json | 9.5 KB | 4 |
| svg | 3.7 KB | 3 |
| Total | 263.9 KB | 10 |
Includes requests done after DOM content loaded.
| Content | Transfer Size | Requests |
|---|---|---|
| html | 0 b | 0 |
| css | 0 b | 0 |
| javascript | 241.2 KB | 1 |
| image | 9.5 KB | 2 |
| font | 71.3 KB | 1 |
| favicon | 0 b | 0 |
| json | 10.3 KB | 6 |
| svg | 3.7 KB | 3 |
| Total | 336.0 KB | 13 |
--enableProfileRun to see where main-thread time went, blocking time and CPU cost per script, module and function, forced reflows and frame stability. The data is collected in one extra run, so the timing metrics of your measured runs stay untouched.Tasks ≥ 50 ms blocking the main thread, collected via the Long Task API.
A long animation frame (LOAF) is a frame that took ≥ 50 ms from input to the next paint. The part beyond the threshold is blocking time, the number that hurts Interaction to Next Paint and Total Blocking Time. Break long tasks up (scheduler.yield(), smaller chunks) or move the work off the main thread. Read more about the Long Animation Frames API.
| Script | Frames | Time running | Blocking (share by run time) | Forced style & layout | Triggered by |
|---|---|---|---|---|---|
| app.js3rd party | 1 | 115.2 ms | 66.9 ms | – | script tag |
| script.js3rd party | 1 | 21.4 ms | 7.6 ms | – | script tag, timer or animation callback |
A frame's blocking time is split between its scripts by their share of the frame's work, capped at each script's own run time — blocking from work no script owns (HTML parsing, browser internals) stays unattributed. The per-script blocking view below uses the same attribution.
1 more long frame carried no blocking time (nothing ran past the 50 ms threshold) — long, but harmless to INP and TBT.
How much each script blocked the main thread, derived from the Long Animation Frame API. Each frame's blocking time is split between its scripts by their share of the frame's work, capped at each script's own run time — blocking from work no script owns (HTML parsing, browser internals) is not attributed (older data credits the script that started the frame). The closest answer to "which script should I fix to improve TBT" the platform exposes.
Third party requests categorised by Third party web version 0.29.2.
Requests by category2
Domains that didn't match any tool in Third party web. If you are sure they are third party domains, please do a PR to that project. You can also fine tune the list using --firstParty.
Transfer size908.7 KB
Content size2.3 MB
Requests54
Calculated using .*whiteready.* (use --firstParty to configure).
| Content | Header Size | Transfer Size | Content Size | Requests |
|---|---|---|---|---|
| html | 0 b | 25.8 KB | 138.2 KB | 1 |
| css | 0 b | 99.3 KB | 578.5 KB | 6 |
| javascript | 0 b | 87.3 KB | 277.3 KB | 13 |
| image | 0 b | 298.5 KB | 293.4 KB | 15 |
| font | 0 b | 124.9 KB | 122.9 KB | 5 |
| favicon | 0 b | 0 b | 0 b | 0 |
| Total | N/A | 635.8 KB | 1.4 MB | 40 |
| Content | Header Size | Transfer Size | Content Size | Requests |
|---|---|---|---|---|
| html | 0 b | 0 b | 0 b | 0 |
| css | 0 b | 0 b | 0 b | 0 |
| javascript | 0 b | 258.6 KB | 939.9 KB | 4 |
| image | 0 b | 0 b | 0 b | 0 |
| font | 0 b | 0 b | 0 b | 0 |
| favicon | 0 b | 0 b | 0 b | 0 |
| plain | 0 b | 260 B | 2 B | 1 |
| json | 0 b | 10.3 KB | 44.3 KB | 6 |
| svg | 0 b | 3.7 KB | 7.3 KB | 3 |
| Total | N/A | 272.9 KB | 991.5 KB | 14 |